- 0 → 1 Design
- Cybersecurity
Cloud Identity Engine: one login for every group
The 0-to-1 feature that let a single security admin route every group of users to the right login method, in one place, without a separate portal per group.
- Role
- Sole Product Designer
- Team
- Solo design, partnered with engineering and sales engineering
- Duration
- 2020 – 2021
- Platform
- Web · PAN-OS
- Year
- 2021
The problem
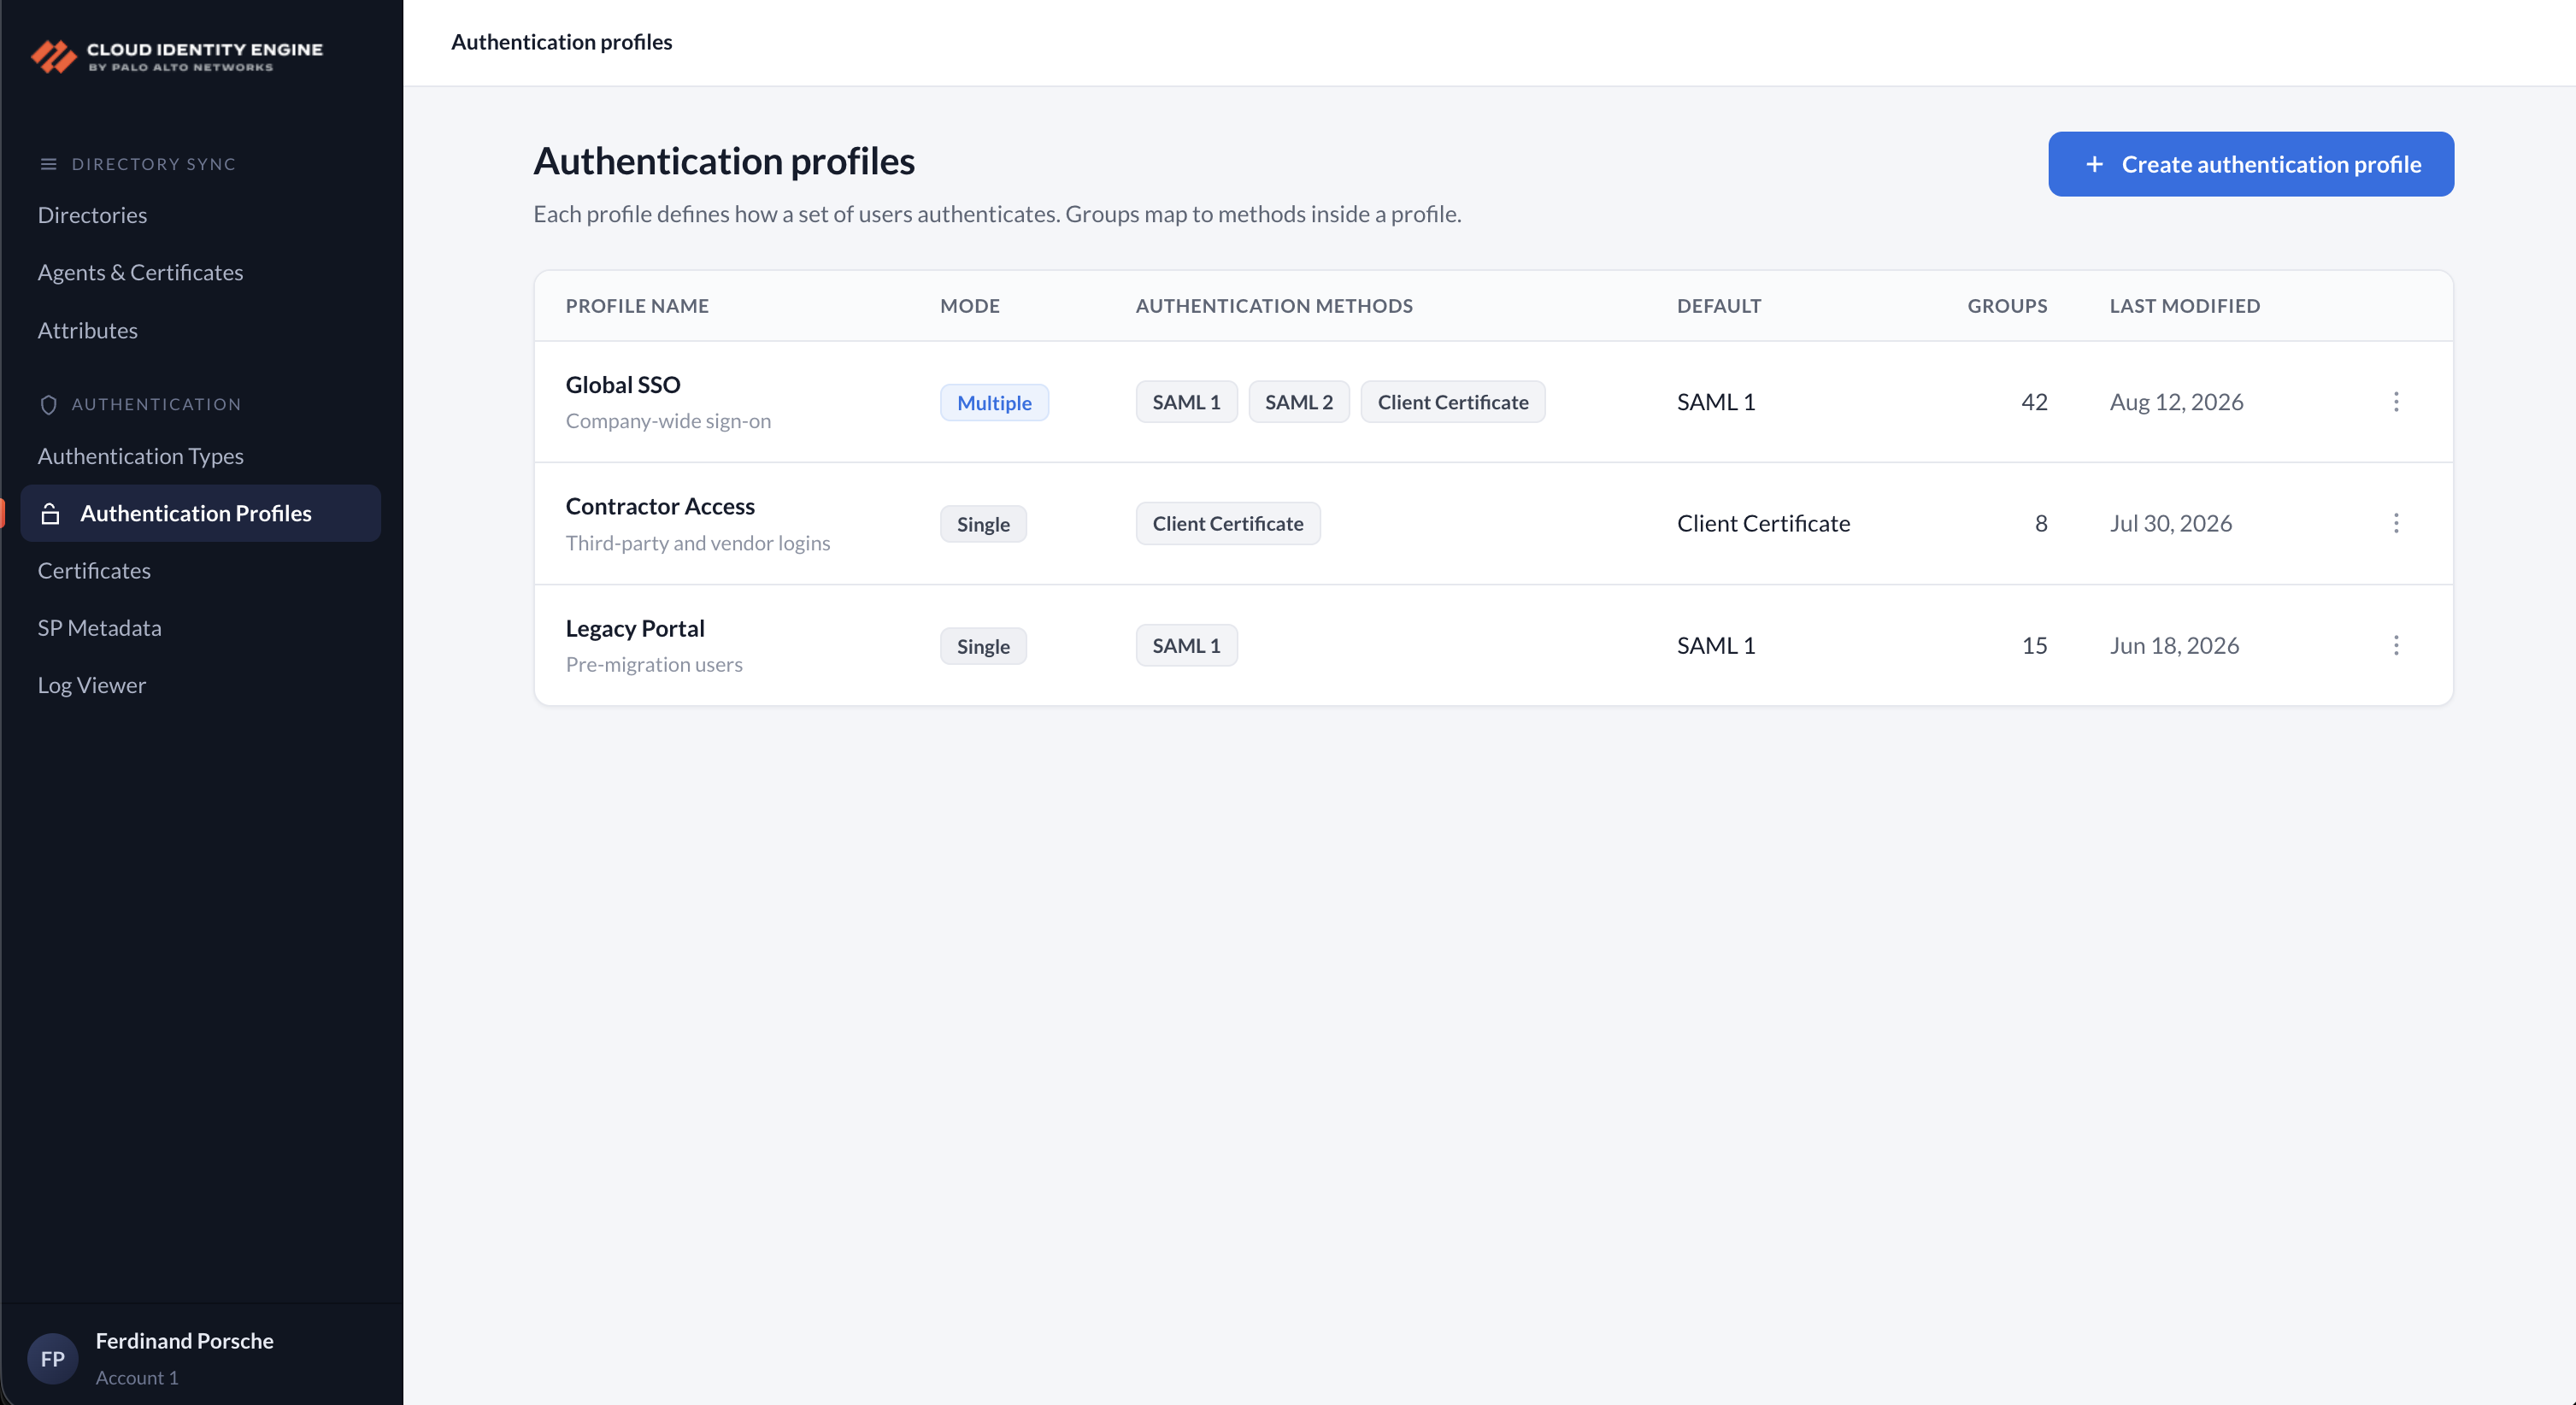
A merger brings a second identity provider, an acquisition a third, contractors a fourth, and admins had only two bad options: a separate login portal per group, or one method forced on everyone.
Process
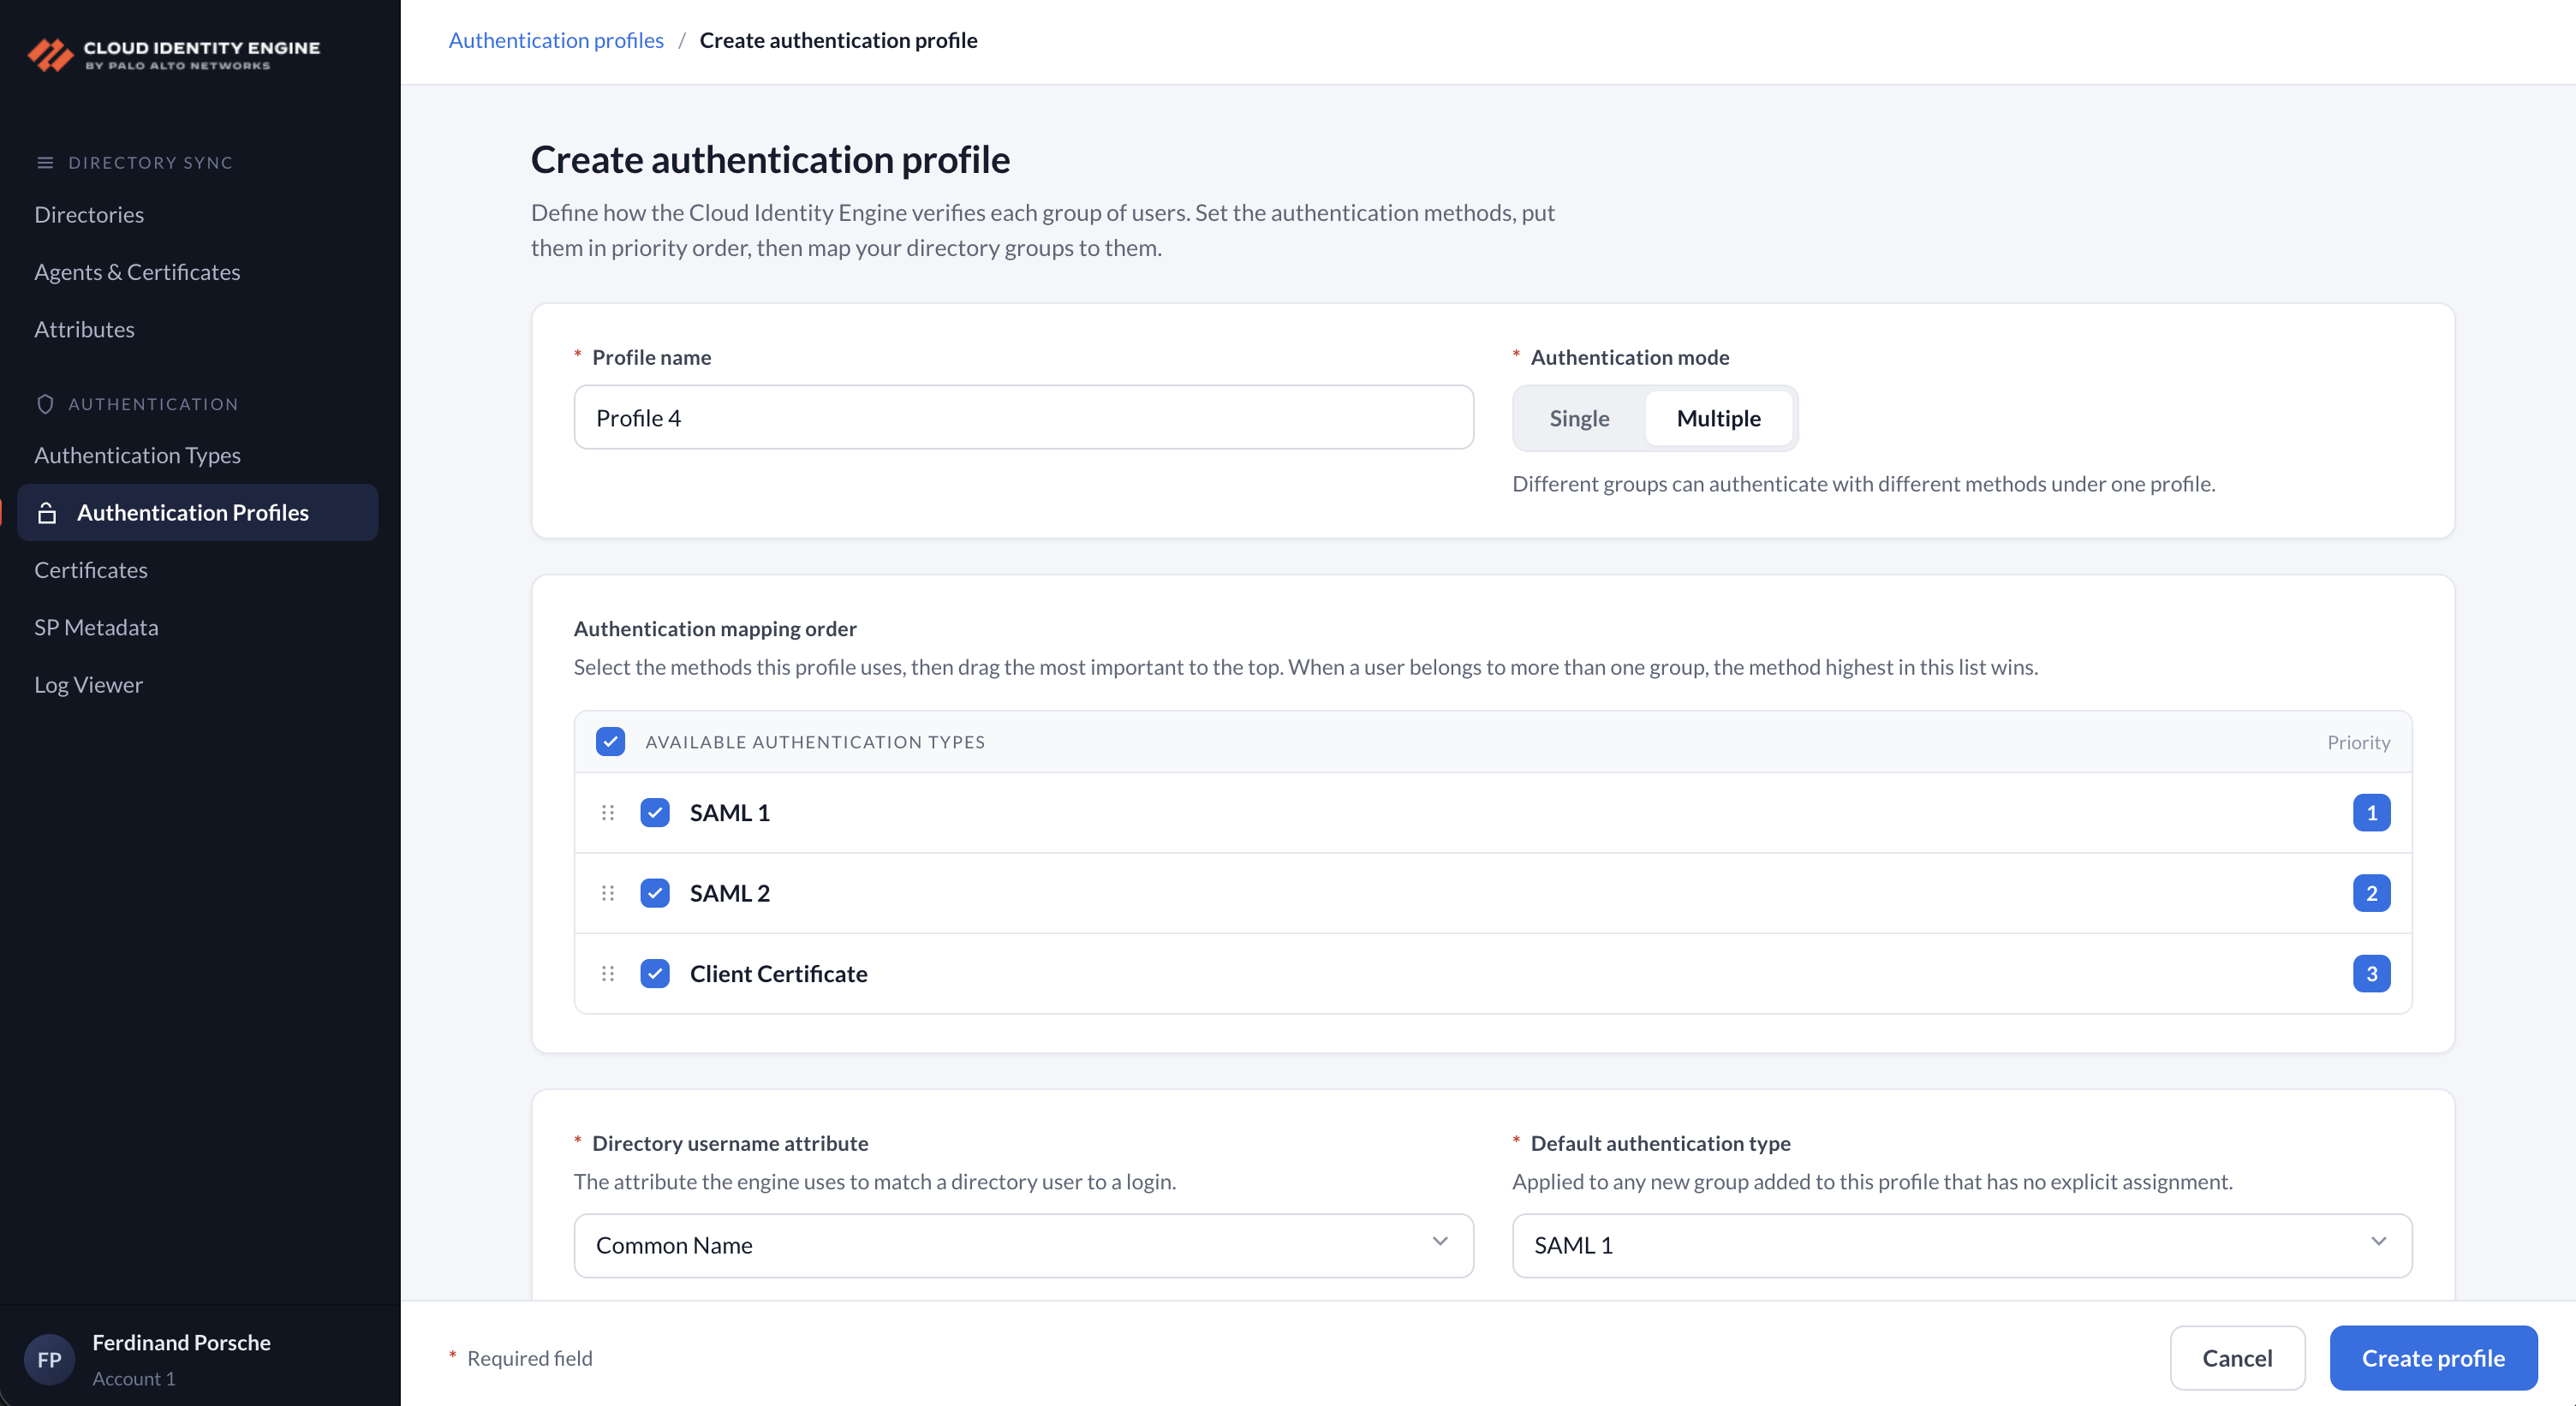
Before drawing a screen I mapped the flow end to end: open the profiles list, name a profile, then choose whether it authenticates one way or several. That single question is where the path forks. One method is a short run to the finish. Several picks up a priority order, a required default, and the group mapping that resolves against them.
Laid out that way, a wizard was clearly the wrong shape. It would have put each of those decisions on its own step, and they are only meaningful next to each other. A priority order means nothing until you can see the groups it resolves, and a default means nothing until you can see what it is catching. Admins configuring something this consequential need to see the whole setup at once, so I kept it on one page and let complexity reveal itself only when it's needed.
Solution
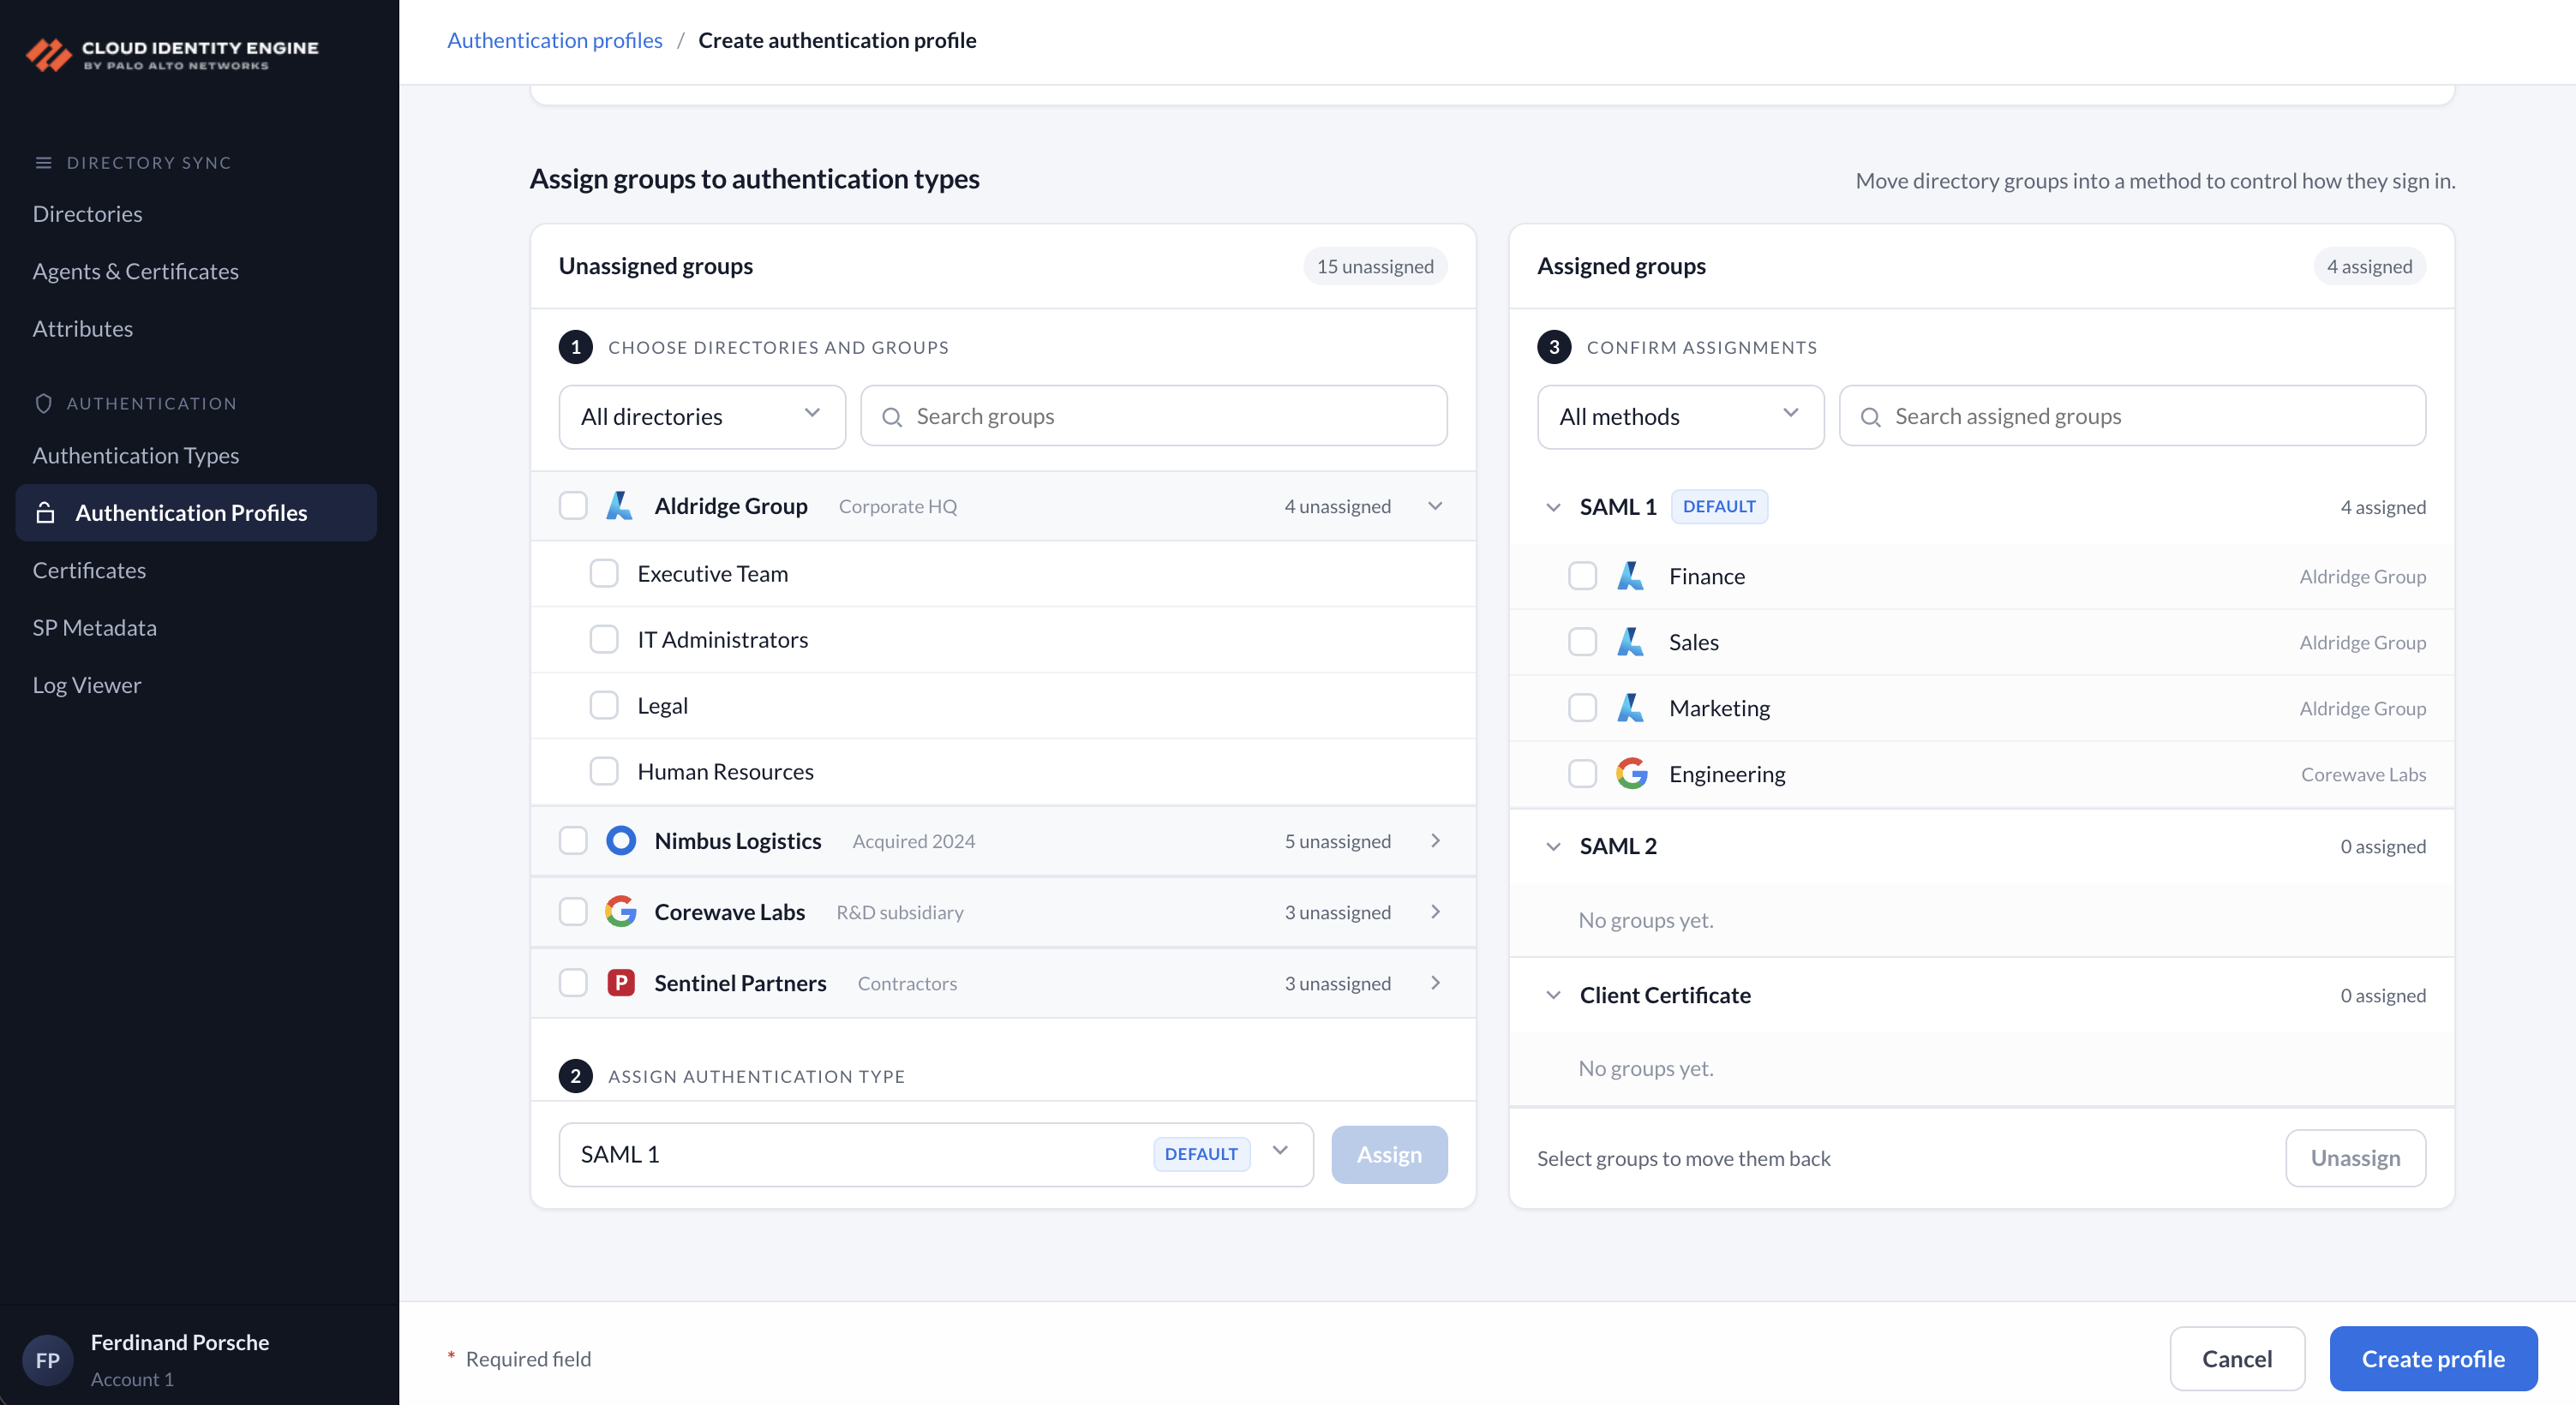
Groups that still need a method sit on the left, assigned ones on the right, so coverage reads at a glance. The fallback and priority order are treated as required security decisions, not optional fields.
Outcome
- Industry first
- Group-based multi-auth in one profile
- PAN-OS 10.2
- Shipped in the Nebula release
- Top 10
- CRN Coolest Cloud Security Tools, 2021